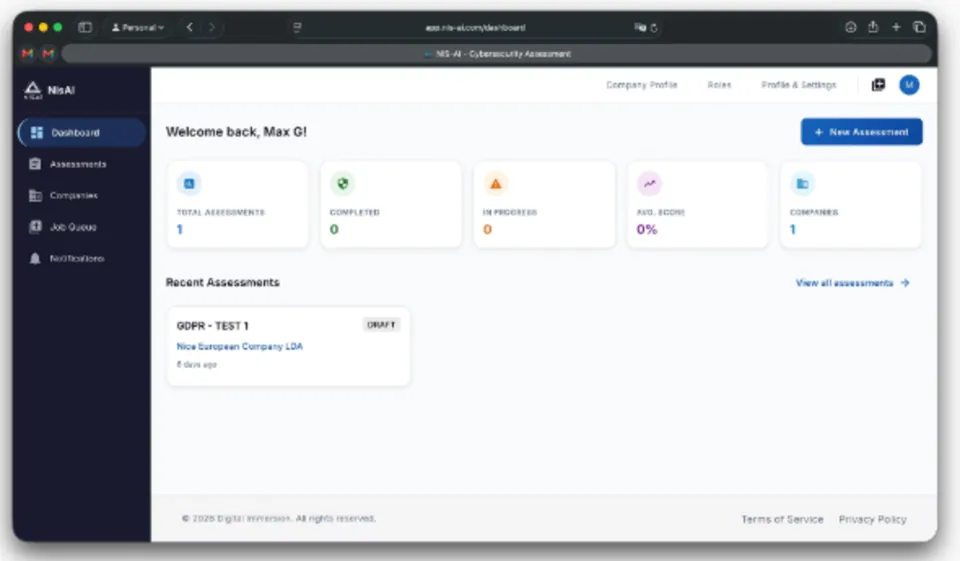
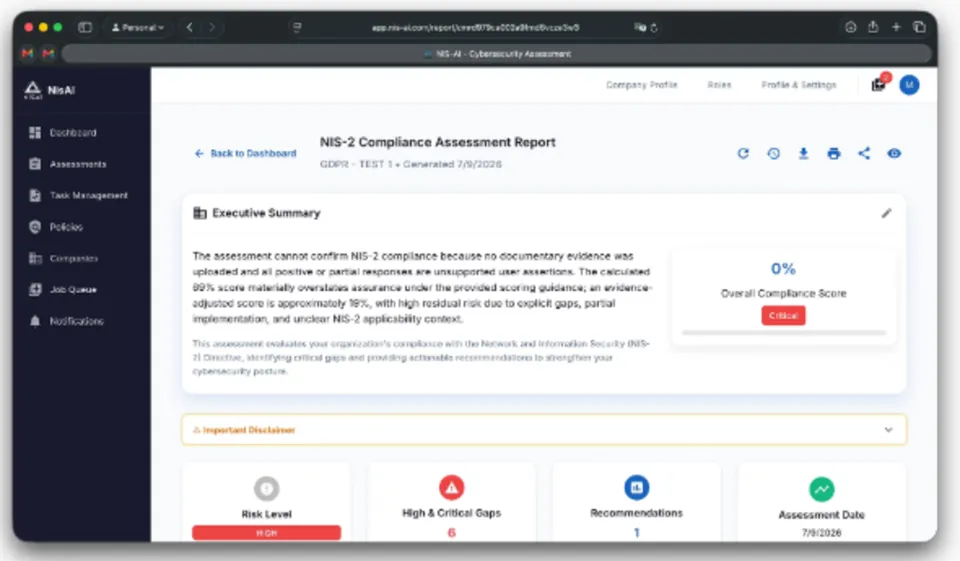
Dashboard
- set up your company's profile
- connect your team members
- assign roles
- monitor your compliance status
 NisAI
NIS2 · CRA · GDPR · DORA · Other regulations by request
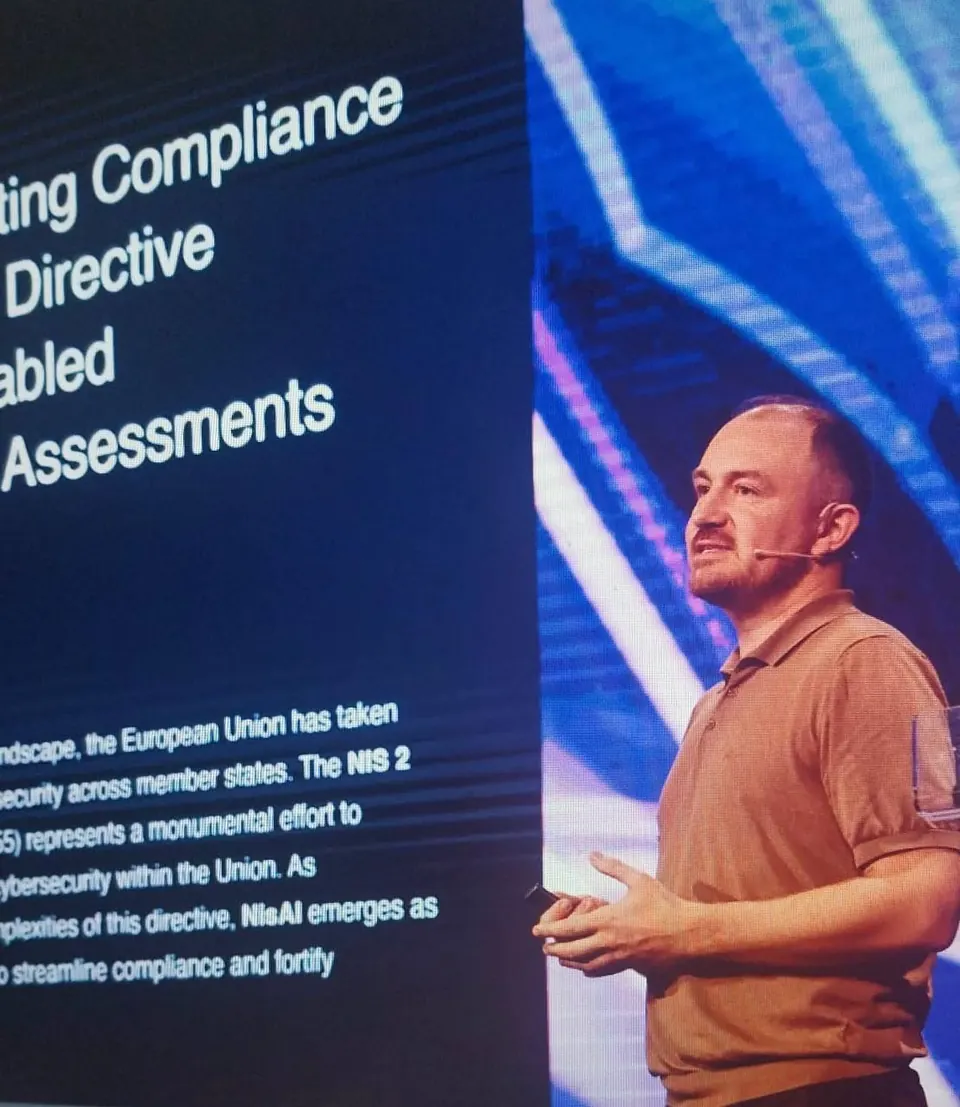
NisAI helps to detect your compliance gaps, develop an actionable plan, draft the policies, and keeps you audit-ready in weeks, not months
Managing frameworks such as NIS2, CRA, GDPR, DORA, and custom regulations by industry, with MiCA, EU AI Act, etc coming soon
Enabling fast and efficient cybersecurity and regulatory compliance assessments for clients through our partnership program
Accelerating due diligence, reducing risk, and monitoring compliance internally and for portfolio companies
Custom questionnaire generated specifically for your company, sector and size
See exactly where you fall short, with actionable remediation steps and policy enhancements to close each gap
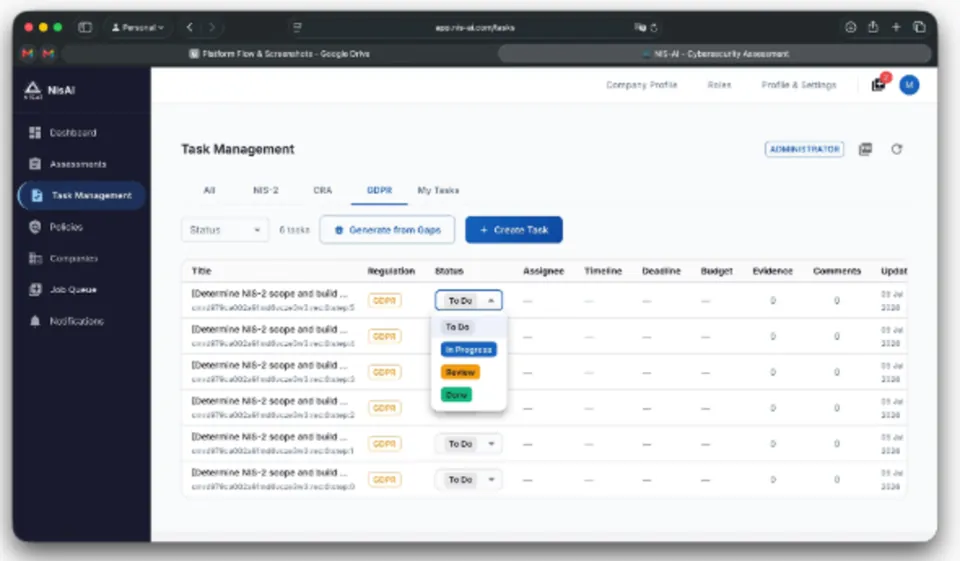
Stay audit-ready as regulations change. Assign tasks, track progress, reassess when needed, and cut audit prep by up to 90%
We work alongside established software, security and institutional partners to deliver compliance you can rely on.


EU-wide and national transpositions. Complete and repeat assessments to save up to 95% of your time and resources
Tailored for financial institutions, streamlined compliance for adjacent spheres, such as insurance and VCs
Protect your AI infrastructure from MCP attacks and security breaches from the latest zero-day CVSs
Data-protection assessments across processing activities, records, and data-subject rights, mapped onto the controls you already have
Company-wide compliance and custom package of supported regulations by request and industry standards
NisAI is backed by the PRR, funded by the Portuguese Republic and the European Union under the New Digital/Technological Products programme.